








Endpoint Security Built for macOS
Advanced threat detection, prevention and response designed specifically for Mac
Mac has become an increasingly important part of the enterprise, from executives and creative teams to software developers working with some of an organization’s most sensitive data and infrastructure. But many endpoint security platforms were originally developed for Windows and later adapted to support macOS. Phorion takes a different approach. Phorion is a modern endpoint detection and response platform built specifically for macOS, combining deep endpoint visibility, behavioral threat detection, proactive protection and incident response in a single lightweight agent. Mac Business Solutions partners with Phorion to help organizations strengthen the security of their Mac environments without sacrificing the performance and user experience that made them choose Apple in the first place.
Security Designed Around macOS
Modern attacks against Mac do not always look like traditional malware. Attackers increasingly use social engineering, malicious developer packages, compromised browser or IDE extensions, credential-stealing tools and legitimate macOS utilities to avoid conventional antivirus detection. Phorion was designed around these threats. Instead of relying exclusively on signatures and known malware hashes, Phorion combines behavioral analysis with detailed macOS telemetry to identify suspicious activity as it happens. The platform uses native Apple technologies along with additional telemetry developed specifically to provide security teams with greater visibility into Mac endpoints. The result is a security platform capable of detecting activity that traditional endpoint tools may overlook while giving administrators the context needed to understand what actually happened.
Detect
Identify Mac-specific threats traditional tools can miss
Phorion combines behavioral detection, macOS-native telemetry and traditional antimalware protection to provide multiple layers of defense. Using Apple’s Endpoint Security Framework along with information from UnifiedLog, Transparency, Consent and Control (TCC) activity, network events, file access and other sources, Phorion can identify suspicious behavior across the endpoint.
This includes threats such as:
- Credential and session-token theft
- Bad actors targeting browser and application data
- Suspicious process execution and process chains
- Malicious scripts and command-line activities
- Persistence mechanisms
- Command-and-control and suspicious network connections
- Developer supply-chain attacks
- Unauthorized access to sensitive files
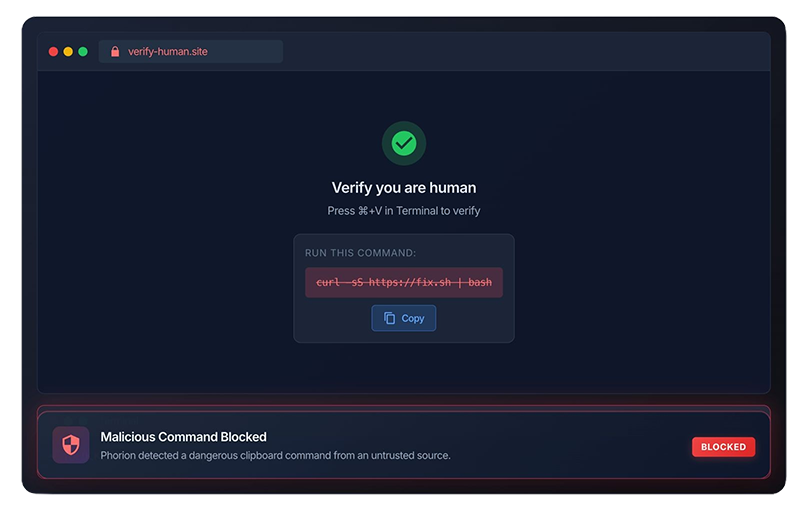
- ClickFix and other clipboard-based social engineering attacks
Phorion also incorporates DoubleYou antimalware technology, adding signature-based malware prevention to its behavioral detection capabilities for defense in depth.
Protect users from ClickFix attacks
ClickFix attacks use social engineering to convince users to copy and paste malicious commands into Terminal or another command-line environment. Phorion’s Clipboard Protection can monitor where clipboard content originated, where it is being pasted and whether the content exhibits potentially dangerous behavior. Depending on organizational policy, suspicious pastes can be audited, presented to the user for confirmation or blocked. This provides an additional layer of protection against attacks that may otherwise rely entirely on a user unknowingly executing a malicious command.
Protect
Move from detecting attacks to preventing them
Detection is important, but preventing an attacker from reaching sensitive data can be even more valuable. Phorion allows organizations to establish controls over which processes are permitted to execute and which applications can access sensitive files. Administrators can protect assets such as browser data, authentication cookies, SSH keys, credentials, configuration files and developer secrets by restricting access to trusted applications and processes. Process controls can also reduce the available attack surface by preventing inappropriate use of tools such as scripting interpreters, command-line utilities and networking tools on systems or within groups that do not require them. Policies can be scoped to specific users, devices or groups, allowing security teams to strengthen protection without unnecessarily restricting legitimate workflows.
Test before you enforce
Security controls can create problems when they are deployed without understanding how employees actually use their Macs. Phorion can use existing endpoint telemetry to evaluate the potential effect of a protection before enforcement. Administrators can review historical activity, identify legitimate exceptions and refine policies before moving from observation to blocking. This telemetry-backed approach helps organizations implement stronger endpoint controls while minimizing disruption to users.
Respond
Investigate and contain threats directly from the platform
When a security incident occurs, Phorion gives security teams tools to investigate and respond without requiring physical access to the affected Mac.
Live Response
Security administrators can establish an audited remote shell to an endpoint to investigate suspicious activity, collect forensic information, execute approved commands, terminate malicious processes or run remediation scripts.
Device Isolation
A compromised Mac can be isolated from the network to prevent lateral movement or additional communication while maintaining the connection required for the security team to continue investigating the device.
Automated Response
High-confidence detections can trigger predefined actions such as terminating processes, isolating endpoints or executing response scripts, helping contain threats before they can progress further
Visual Attack Analysis
Phorion can connect related processes, files, network activity and alerts into visual attack graphs, helping analysts understand how an incident developed and determine what systems or data may have been affected.
Monitor
See what is actually running across your Mac environment
Protecting an endpoint starts with knowing what is on it. Phorion maintains detailed visibility into applications, packages, extensions, persistence mechanisms, operating-system versions and security configurations across the Mac fleet. Organizations can use this information to identify vulnerable devices, investigate emerging threats and answer questions that would otherwise require manually inspecting individual Macs.
Application and Software Inventory
Maintain visibility into installed applications across managed endpoints for security investigations, software management and compliance.
Developer Package Tracking
Phorion can inventory packages installed through ecosystems such as npm, Homebrew and pip, helping security teams identify affected endpoints when a malicious or compromised dependency is discovered.
IDE and Browser Extensions
Track extensions installed in environments such as Visual Studio Code, Cursor and web browsers. If a malicious extension is identified, security teams can quickly determine where it exists within the organization.
Persistence Monitoring
Identify launch agents, launch daemons, login items and other mechanisms capable of allowing software or malware to persist across restarts.
Security Posture and Patch Visibility
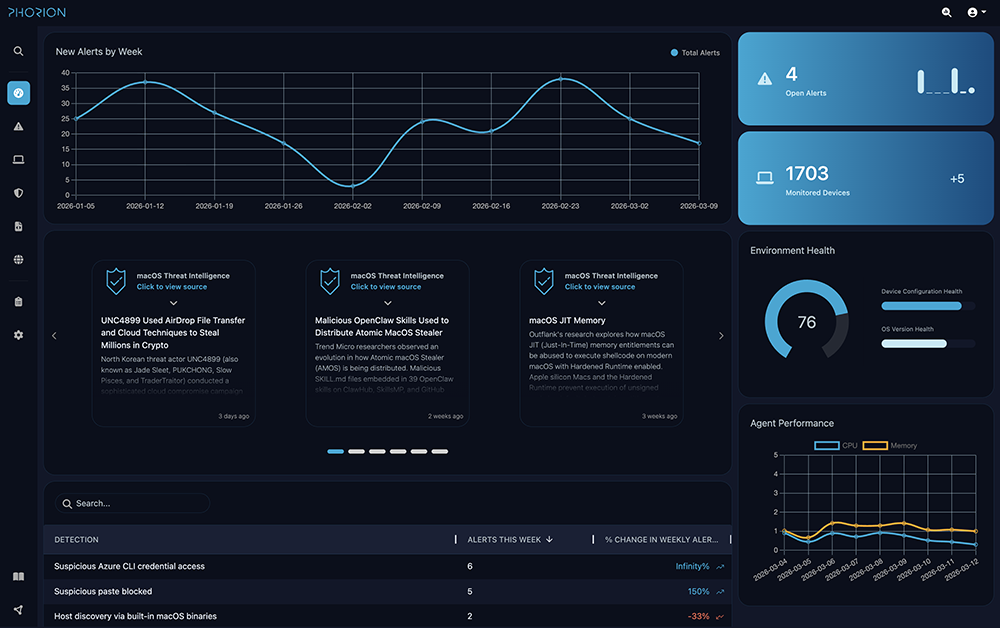
Monitor macOS versions, security configuration and other risk factors to identify systems requiring attention. Phorion’s device health scoring helps security teams prioritize remediation across larger fleets.
Fleet-wide Investigation with osquery
Built-in osquery capabilities allow administrators and security analysts to query endpoint state using SQL, providing a powerful way to investigate processes, software, network connections, persistence mechanisms and other endpoint information across the organization.
Complete Visibility for Security Teams
Understand the data behind the alert
Endpoint security platforms sometimes provide an alert without exposing enough information for administrators to understand why it was generated. Phorion emphasizes transparency. Security teams can access raw endpoint telemetry through Phorion’s built-in SIEM, examine the logic behind detections and investigate the underlying events associated with an alert. Organizations can also create custom detection rules, adjust severity and thresholds, establish allowlists and tune detections around their own infrastructure and threat model. This makes Phorion useful not only as an endpoint protection platform but as a source of detailed Mac security intelligence for experienced security teams.
Built with Privacy in Mind
Understand the data behind the alert
Collecting detailed endpoint telemetry requires careful handling of user and organizational data. Phorion includes controls designed to limit unnecessary exposure of sensitive information. Secret-scrubbing capabilities can remove credentials, tokens and other protected values from telemetry before that information leaves the endpoint. Clipboard Protection also incorporates safeguards for privacy-sensitive applications such as password managers, while administrators can control how much clipboard content—if any—is included in security telemetry. Phorion supports regional data residency requirements and is GDPR compliant.
One Lightweight Agent
Security without turning Mac into a Windows endpoint
Security software should not become another source of endpoint problems. Phorion combines threat detection, prevention, endpoint visibility and incident response within a single macOS agent rather than requiring a collection of separate point solutions. The platform is designed to minimize resource consumption, and administrators can monitor the CPU and memory utilization of the agent across their fleet. Phorion can also be deployed through Jamf, Kandji or other device management platforms, allowing organizations to incorporate endpoint security into their existing Mac deployment and management workflows.
Why Phorion + Mac Business Solutions?
Deploying endpoint security is not simply a matter of installing another agent. The platform needs to complement the organization’s device management strategy, security requirements and existing Mac workflows. As an Apple Premier Partner with more than 35 years of experience working with Apple technology, Mac Business Solutions helps organizations design, deploy and support Apple environments at scale.